What if your encryption's randomness was something you could actually watch happen?
What if your encryption's randomness was something you could actually watch happen? Most random numbers used in cryptography are generated deterministically from an initial source of entropy. If that seed is predictable or compromised, the randomness collapses, and so does the security built on top of it.
I wrote recently about "harvest now, decrypt later," the risk of encrypted data being stored today and cracked once quantum computers are powerful enough. A stronger encryption algorithm won't compensate for insufficient or predictable randomness used to generate its keys.
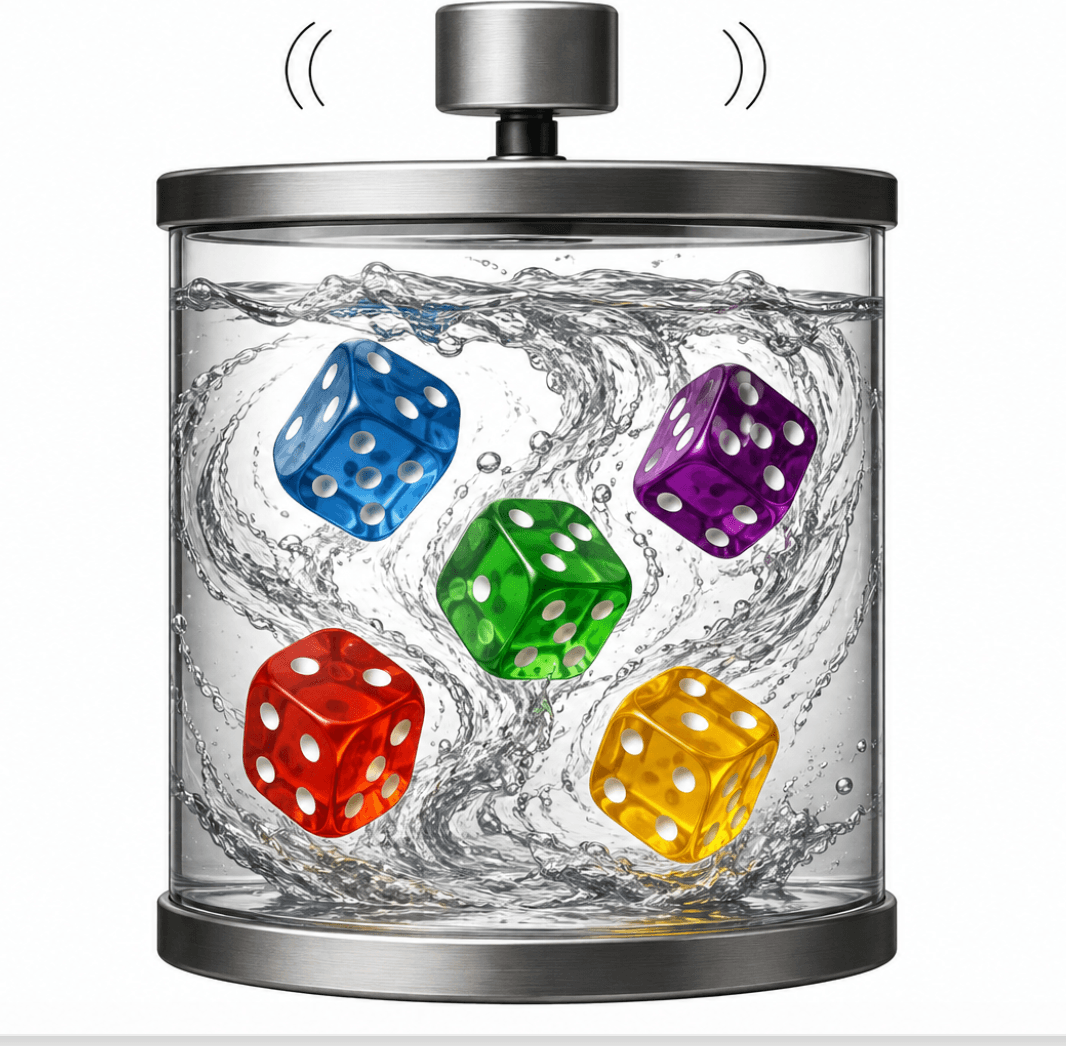
To solve that problem, Real Random LLC generates entropy from a physical process rather than relying solely on a deterministic algorithm: physical dice, tumbling through viscous fluid inside patented hardware, in motion that's extremely difficult to model or predict computationally. Optical sensors read the position, rotation, and collision of the dice in real time, converting that physical chaos directly into entropy.
I met the team recently (Doug Hill and Colin Barnett), and it was a genuinely impressive conversation. The dice themselves are colourful and oddly mesmerising, even just in photos, a fun, tangible way to demonstrate something usually invisible and abstract.
The hardware is the product. The dice, the fluid, the optical sensors, that's where the actual entropy comes from, and it's what a team eventually buys and runs on their own premises as a rack-mounted appliance or portable device. The REST API is simply a way to access that same physical hardware remotely first, useful for testing and prototyping before committing to a local setup.
Standards and post-quantum migration requirements are also putting more attention on how cryptographic randomness is generated, validated and protected. Good timing for security and engineering teams to see what real physical entropy looks like, rather than trusting a black box.
Real Random's developer portal is open for registration now: https://lnkd.in/e54vvU-e
We already registered - your turn. It's a simple way to see what physical entropy looks like in practice.
Sources: Real Random (real-random.com); AMD Security Bulletin (AMD-SB-7055, CVE-2025-62626); Keyfactor/IEEE, "Factoring RSA Keys in the IoT Era."